Can AI Help Security Teams Detect Threats Before They Escalate?
- Security teams receive a continuous stream of events from endpoints, networks, cloud services, applications, and user accounts. Deciding which alerts matter and how they connect is the harder task.
- AI-assisted detection compares current activity with established behavior, correlates related alerts, and helps analysts interpret technical evidence. Rule-based tools remain essential for known attack patterns.
- The ENISA Threat Landscape 2026 identifies ransomware as the most impactful incident type in the short term, and critical infrastructure operators face added complexity due to legacy and operational technology systems.
- High-impact response decisions require human oversight, and AI components within security workflows must be secured themselves.
Security Operations Centers monitor activity across endpoints, networks, cloud services, applications, and user accounts, and the events these systems produce often need investigation before their significance becomes clear. Modern tooling generates alerts easily. Recognizing which ones matter and how they connect is the harder task for security teams, and it is where AI-assisted threat detection is increasingly being applied.
Why a Single Alert Rarely Settles Anything
Traditional detection tools rely on predefined rules and known indicators of compromise. They remain essential for identifying established attack patterns, but they struggle when malicious activity does not match an existing signature or when individual events appear harmless in isolation. An employee account accessing an unfamiliar server outside normal working hours might be legitimate maintenance or a compromised credential. The alert alone cannot establish which.
An analyst needs additional context: the account’s usual activity, the device involved, recent authentication attempts, and the sensitivity of the accessed systems. Assembling that context across separate tools takes effort, and this is where AI-assisted analysis can contribute. It makes the underlying information more accessible and connected, while the judgment stays with the analyst.
What AI Adds to Detection and Investigation
Machine learning models can identify behavioral deviations by comparing current events with established patterns, detecting unusual activity in user behavior, network communication, or system access without relying exclusively on known malicious signatures. Event correlation helps analysts understand whether separate alerts might be related: an unusual authentication attempt, a permission change, and unexpected data transfers may carry more significance together than individually.
Large language models are also entering this space. An analyst investigating a suspicious PowerShell command might use an AI assistant to explain its behavior, identify potentially dangerous operations, and suggest which related events deserve closer examination. These capabilities can reduce the effort required to interpret complex security information, but their effectiveness depends on the quality of the underlying data and the controls governing their use. An AI-generated explanation is not proof of malicious activity. A plausible interpretation can still be incorrect, incomplete, or based on misleading evidence.
Why Critical Infrastructure Raises the Stakes
The consequences of a cybersecurity incident depend on the environment in which it occurs. In a hospital, a disruption could affect access to clinical information, connected medical devices, or systems needed to coordinate patient care. Critical infrastructure also introduces technical complexity: organizations may operate legacy equipment alongside modern cloud applications, connected devices, and operational technology systems that were not designed to work together.
The ENISA Threat Landscape 2026, which covers incidents from January to December 2025, identifies ransomware as the most impactful incident type in the short term and notes that cyber dependencies expand the attack surface. In the incidents it analyzed, 73% of targeted organizations were essential or important entities under NIS2, and public administration remained the most targeted sector at 32% of cases. The report also expects emerging AI models to be increasingly used to support malicious operations.
For infrastructure operators, effective threat detection requires more than identifying malicious software. Security teams must understand how an incident could affect connected systems and essential operations. AI-assisted analysis can help bring those relationships into focus, but the final assessment still requires knowledge of the organization’s infrastructure and operational priorities.
Where Human Oversight Has to Stay
An AI system that identifies suspicious activity is different from one that decides how an organization should respond. An incorrect classification has consequences in either direction. A false negative may allow malicious activity to continue unnoticed. A false positive may lead analysts to investigate harmless behavior or, in systems with automated response capabilities, interrupt legitimate operations.
Human oversight remains especially important for high-impact decisions such as isolating critical systems or restricting access to operational infrastructure. Adversarial manipulation adds another consideration: attackers may attempt to evade detection models, contaminate the data used for analysis, or exploit weaknesses in AI assistants that process untrusted information. Adding AI to a security workflow creates new capabilities and introduces components that must be secured themselves.
For this reason, the value of AI-assisted cybersecurity should be measured by what happens after an alert appears. Can the team understand the threat, determine which systems are affected, and respond without creating unnecessary disruption? Detection accuracy matters, but so do false-positive rates, investigation time, explainability, and the consequences of an incorrect recommendation.
How ASSIST Software Contributes Through REINFORCE and LLM4CIP
At ASSIST Software, we are exploring these challenges through European research and innovation projects focused on cybersecurity in critical environments.
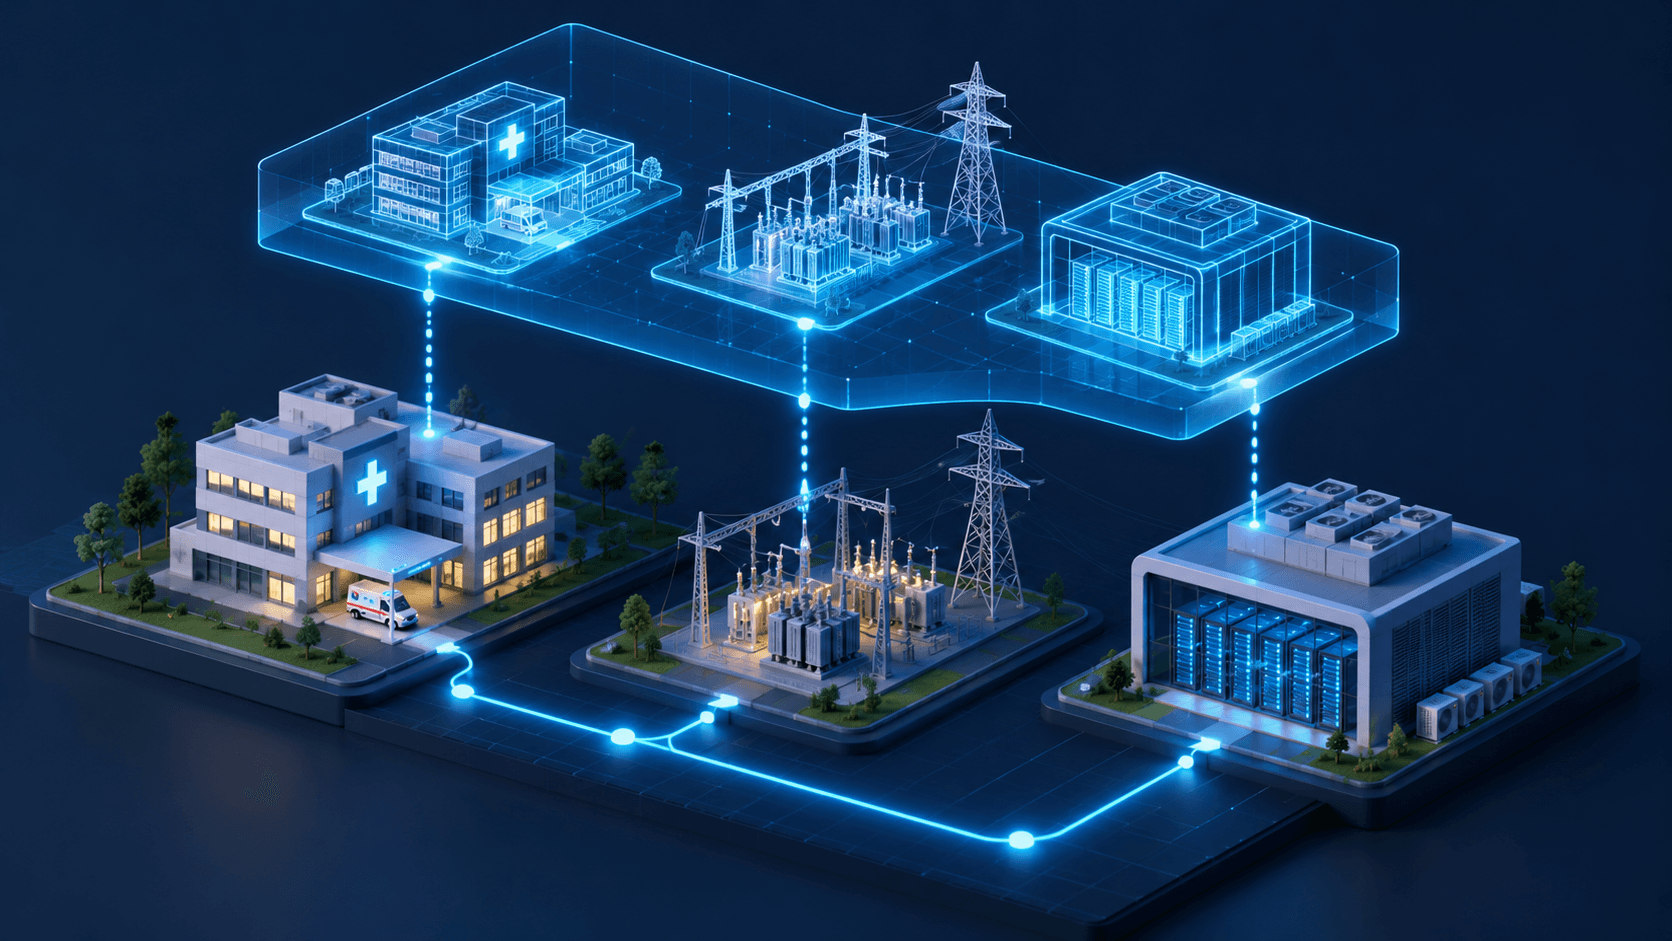
As the coordinator of REINFORCE, ASSIST Software contributes to developing an AI-enhanced cybersecurity ecosystem for European healthcare providers, focusing on AI-assisted monitoring, Security Operations Center capabilities, threat analysis, and coordinated incident response. ASSIST Software also coordinates LLM4CIP, a Digital Europe project investigating how large language models, digital twins, and secure cloud infrastructure can support cybersecurity preparedness across critical infrastructure sectors, addressing threat detection, contextual risk analysis, and incident response in complex IT and operational technology environments.
Both initiatives aim to develop AI capabilities that support security professionals while accounting for the operational requirements of the environments they protect. If you are working on cybersecurity challenges in healthcare or critical infrastructure, we would like to hear about what you are building.